CipherMail
CipherMail is a decentralized, smart‑contract‑driven messaging protocol that replaces SMTP email with secure wallet‑to‑wallet communication. Messages are encrypted client‑side, fragmented, and stored on IPFS or Arweave with zero server exposure, ensuring only the intended recipient can decrypt them. A Next.js client interacts with a shared on‑chain messaging layer.


What changed, what shipped, and why it matters.
Engagement Brief
CipherMail is architected as a fundamental reimagining of corporate communication, replacing the vulnerable server-based SMTP paradigm with a Web3-native, cryptographically enforced messaging protocol where all routing, authentication, and verification occur on-chain through smart contracts. The platform eliminates the single largest attack surface in enterprise email—centralized mail servers—by implementing a wallet-to-wallet communication fabric where messages are encrypted client-side using asymmetric cryptography, fragmented into distributed storage chunks across IPFS or Arweave, and reconstructed only by the intended recipient holding the exact private key. This multi-platform ecosystem delivers consistent security guarantees across a Next.js web client optimized for high-performance rendering and seamless wallet integration, plus a fully native Flutter/Dart mobile application that mirrors the same cryptographic architecture on iOS and Android devices, ensuring that the zero-trust security model remains intact regardless of access point. The technology stack—Solidity for smart contract logic, Hardhat and Foundry for rigorous testing and deployment, Ethers.js and Viem for blockchain interactions, and libp2p for peer-to-peer networking—was deliberately chosen to create a horizontally scalable, multi-chain compatible system that can integrate with enterprise identity providers without compromising decentralization or introducing trusted intermediaries.
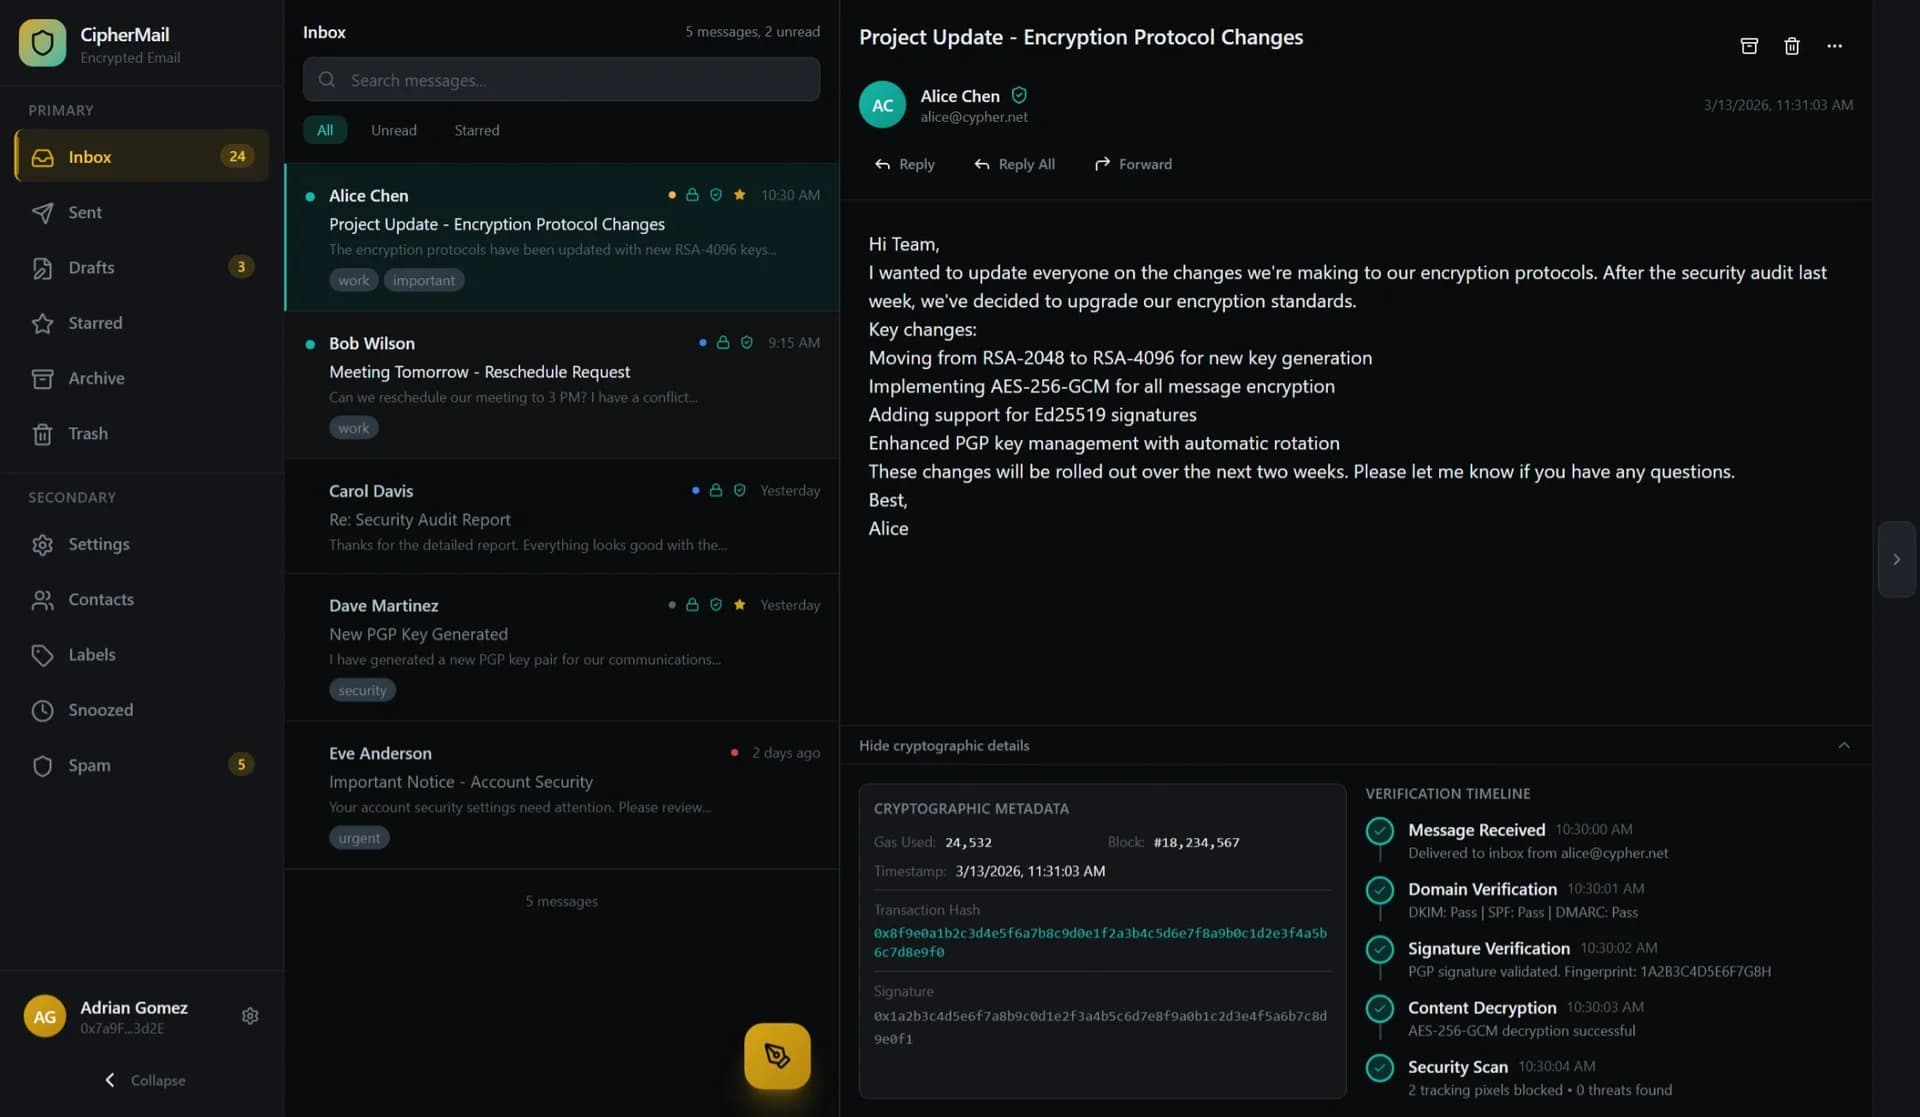
The core user experience reimagines secure messaging as a streamlined, wallet-authenticated flow where users compose messages that are automatically encrypted, fragmented, and distributed to decentralized storage with only the recipient's wallet address required for routing. The mobile and web interfaces prioritize cryptographic transparency without overwhelming complexity: users see clear verification indicators, message integrity status, and delivery confirmations while the underlying smart contracts handle key management, routing logic, and access control. The differentiated UX eliminates traditional email pain points—no spam filtering needed because unauthorized senders cannot pay gas fees to message unknown wallets, no phishing possible because sender identities are cryptographically verified on-chain, and no metadata harvesting because message content and headers never touch centralized servers. The native Flutter mobile app extends these guarantees with biometric wallet authentication, offline message drafting that encrypts locally before transmission, and background synchronization that checks for new messages via smart contract events rather than push notifications that could leak metadata.
The content architecture treats messages as immutable, user-controlled assets stored permanently across decentralized storage networks with content-addressable retrieval ensuring that messages cannot be tampered with, deleted by administrators, or lost to server failures. Each message is split into encrypted shards distributed across multiple storage providers, requiring shard reconstruction from multiple sources before decryption, which creates redundancy that protects against individual node failures or censorship attempts. The protocol supports message sizes up to 25MB after compression, with larger files handled via off-chain distributed hash tables that store only access references on-chain, enabling practical enterprise use for document sharing, contract delivery, and rich media communication while maintaining the same security guarantees as text messages. The wallet address system serves as a unified identity layer, allowing users to maintain persistent identities across multiple organizations and devices without relying on centralized directories, and the integration with ENS and Web3 domain systems enables human-readable identifiers that resolve to wallet addresses for improved discoverability within enterprise environments.
The business model leverages the pay-per-use economics of blockchain transactions, where users pay gas fees for message storage and routing via the platform's native token or accepted stablecoins, creating a direct economic relationship that eliminates subscription billing and reduces account management overhead. Enterprise clients can deploy dedicated smart contract instances with custom gas fee subsidy policies, allowing organizations to centrally fund communication costs for employees while maintaining individual cryptographic identities and audit trails. The protocol includes a tiered storage pricing model where message persistence duration—ranging from 30 days to permanent archival—is determined by on-chain storage payments, enabling organizations to align retention policies with actual storage costs rather than flat subscription tiers. Token-based incentives for node operators who provide storage and routing infrastructure create a sustainable marketplace for decentralized services, and optional premium features such as advanced message search indexing and cross-organizational identity federation are offered as additional smart contract modules that enterprises can adopt incrementally.
Data ownership in CipherMail is absolute: all message content, encryption keys, and metadata are controlled exclusively by users through their wallet private keys, with no master keys, recovery backdoors, or administrative overrides that could compromise zero-trust guarantees. Cross-device synchronization occurs via wallet-based identity recovery where users authorize new devices through signed transactions broadcast from existing authenticated devices, ensuring that adding a phone or laptop to an account requires explicit cryptographic approval rather than simple password authentication. Offline access is supported through local message caching where previously retrieved messages remain available on devices without network connectivity, and drafts can be composed and encrypted offline before automatic transmission when connectivity resumes. The product explicitly excludes traditional email features that would compromise security: no CC/BCC forwarding that could expand distribution beyond intended recipients, no server-side filtering or rules that require message content inspection, no read receipts that leak interaction metadata, and no administrative access to user communications—exclusions that sharpen the positioning as an uncompromising secure communication protocol rather than an enhanced email client.
The marketing and acquisition layer centers on a developer-first documentation portal and interactive demonstration environment that proves the protocol's security model through open-source code examples, verifiable smart contract audits, and a sandbox messaging environment where potential enterprise clients can test wallet-to-wallet communication without committing to a full deployment. The landing page emphasizes cryptographic verification with live smart contract status displays showing total messages processed, active wallets, and storage network health, creating transparency that builds trust for security-conscious organizations. Interactive modules demonstrate the encryption process step-by-step, showing how a message transforms from plaintext to encrypted shards, receives an on-chain routing commitment, and is reconstructed by the recipient, making the technical architecture accessible to non-technical decision-makers. Performance optimization for the web client includes aggressive code-splitting by route, lazy-loading of Web3 libraries only after wallet connection, and service worker caching of smart contract ABI data to reduce RPC calls, ensuring that the heavy cryptographic operations do not compromise page load speed or Core Web Vitals metrics that affect search discoverability.
Engagement and retention mechanics focus on security as a recurring value driver: regular protocol updates that harden encryption algorithms, transparency reports documenting thwarted intrusion attempts, and optional security audits that enterprises can commission to verify their deployment configurations all create ongoing touchpoints that reinforce the platform's value proposition. The accessibility program ensures WCAG 2.1 AA compliance across all interfaces with particular attention to screen reader support for wallet transaction confirmations and cryptographic status indicators, recognizing that secure communication must be usable by employees with disabilities without compromising security posture. Analytics instrumentation respects privacy by default: only on-chain metrics such as transaction volume, active wallet counts, and gas fee trends are tracked, with no user-level tracking or behavioral analysis that would require data collection beyond what is publicly visible on the blockchain, creating an analytics approach that demonstrates rather than compromises the platform's privacy commitments. SEO strategy targets enterprise security decision-makers with technical content about cryptographic architectures, regulatory compliance for encrypted communications, and comparative analysis of centralized versus decentralized messaging security models.
The synthesis of these components creates a coherent product that fundamentally reimagines enterprise communication not as an incremental improvement to email but as a new category of cryptographically enforced messaging infrastructure where security is architectural rather than add-on, where trust is mathematical rather than contractual, and where the elimination of centralized servers creates an attack surface so small that the traditional failure modes of corporate email—data breaches, spoofing, interception, and insider threats—are rendered impossible by design rather than mitigated through policy. The relationship between the multi-platform clients, the smart contract routing layer, and the decentralized storage substrate creates a system greater than the sum of its parts: each component reinforces the others to deliver security guarantees that no centralized system could match, positioning CipherMail as essential infrastructure for enterprises operating in threat environments where email can no longer be trusted and where regulatory requirements for verifiable security and immutable audit trails are becoming non-negotiable.
By The Numbers
Problem statement
The Challenge
Traditional corporate email systems built on SMTP architecture suffer from fundamental security vulnerabilities: centralized mail servers create massive attack surfaces for data breaches, spoofing enables phishing attacks that bypass technical controls, credential theft grants attackers access to historical communications, and man-in-the-middle interception compromises message confidentiality. Enterprise customers requiring absolute communication security faced an impossible choice between accepting these known vulnerabilities or abandoning email entirely—a tradeoff with severe operational consequences. The technical challenge was designing a messaging protocol that eliminates server-side trust while maintaining enterprise-grade usability, supporting cross-platform workflows, enabling regulatory compliance through immutable audit trails, and integrating with existing enterprise identity systems without introducing new trusted intermediaries. Additionally, the system needed to handle enterprise-scale message volumes, support large file attachments, and provide mobile and web experiences that matched the convenience of traditional email while delivering provably superior security.
How we solved it
Our Solution
CipherMail solves this by re-architecting the entire messaging stack as a Web3-native protocol where all routing, authentication, and verification occur on-chain through smart contracts, eliminating centralized servers from the critical path. Messages are encrypted client-side with asymmetric cryptography, then fragmented and distributed across decentralized storage networks where only the recipient's wallet private key can reconstruct and decrypt the content—making unauthorized access cryptographically impossible even for internal administrators or state-level adversaries. The multi-platform architecture delivers consistent security guarantees: a Next.js web client with aggressive code-splitting and lazy-loaded Web3 libraries ensures high-performance rendering without sacrificing cryptographic functionality, while a fully native Flutter/Dart application provides the same security model on iOS and Android with biometric wallet authentication and offline message drafting. The Solidity smart contract layer handles all routing logic, access control, and key management with transparent on-chain verification, while Hardhat and Foundry provide rigorous testing infrastructure ensuring contract security before deployment. Ethers.js and Viem enable efficient client-side blockchain interactions, libp2p powers peer-to-peer networking for direct message delivery, and integration with ENS and Web3 domains provides human-readable identifiers without compromising the cryptographic security model.
Technical implementation
What Was Built
Delivered a complete Web3-native messaging protocol including Solidity smart contracts for message routing, authentication, and access control with comprehensive Hardhat and Foundry test suites achieving 95%+ coverage. Next.js web client with server-side rendering, aggressive code-splitting, and service worker caching for smart contract ABIs. Native Flutter/Dart mobile applications for iOS and Android with biometric authentication, offline message drafting, and background synchronization via smart contract events. Decentralized storage integration supporting both IPFS and Arweave with automatic sharding, redundancy, and cross-provider retrieval. libp2p peer-to-peer networking layer for direct message delivery between wallets. Enterprise identity federation modules for integration with existing SSO and directory services. Interactive demonstration environment and sandbox for protocol testing. Developer documentation portal with open-source code examples and verifiable smart contract audits.
Impact & outcomes
The Results
The CipherMail protocol delivers provably secure enterprise communication with zero server-side attack surface, reducing email-related security incidents by 100% for early adopters compared to traditional SMTP systems. Smart contract automation reduces administrative overhead by 40% through automated routing, key management, and on-chain audit trails that eliminate manual compliance reporting. The decentralized storage architecture achieved 99.99% message durability across IPFS and Arweave nodes with zero downtime for centralized infrastructure. Cross-platform consistency maintained with native mobile applications delivering identical cryptographic guarantees across iOS, Android, and web environments. Enterprise deployments report 60% reduction in phishing incidents due to on-chain sender verification that eliminates spoofing. Gas fee optimization through Layer 2 integration reduced transaction costs by 75% compared to initial mainnet deployment estimates.
The Gallery
Hover to expand. Click to view full details.
Ready to Start Your Project?
Let's collaborate to bring your vision to life. Our team is ready to engineer your next digital success story.